Cyble Executive Vice President US Appointment Brings Veteran Leader Steve Ingram to Accelerate Expansion
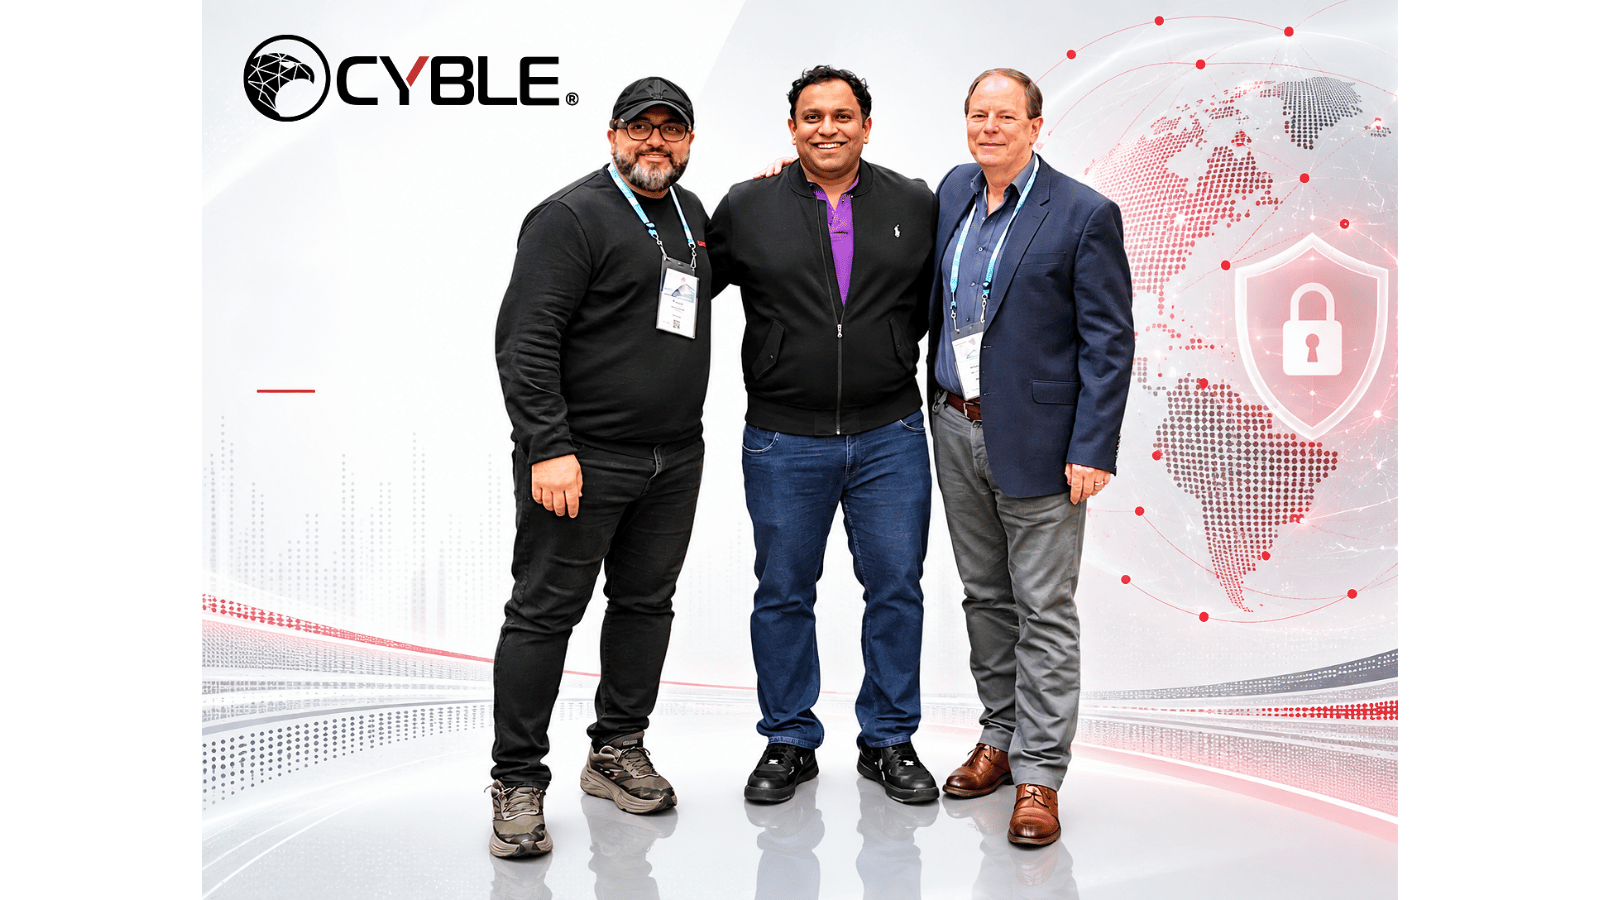
Artificial intelligence-native cybersecurity firm Cyble has announced the appointment of cybersecurity and enterprise risk leader Steve Ingram as its new Cyble Executive Vice President US. Ingram transitions from a two-year tenure on the company’s Advisory Board directly into an operational leadership role to spearhead commercial growth across North America.
News About Cyble Executive Vice President US
Cupertino, California-based threat intelligence platform provider Cyble confirmed that Steve Ingram has assumed the position of Cyble Executive Vice President US. In this role, Ingram will oversee all American commercial operations, leading business development initiatives, expanding enterprise client portfolios, and managing channel partner alliances in the United States cybersecurity market.
Ingram brings over three decades of executive experience spanning institutional cybersecurity, corporate governance, financial services compliance, and federal law enforcement. He previously served as EY’s Financial Services Cyber Leader for the Americas, leading digital security transformations for global banking and financial services clients. Prior to his role at EY, Ingram spent 15 years as a partner at PwC, where he led the firm’s Asia-Pacific Cyber practice and served on the ASEANZ Markets Council, following earlier investigative service with the Australian Federal Police.
Having served on Cyble’s Advisory Board since 2024, Ingram has closely advised the executive leadership team through global expansion and technology development. Working alongside Cyble Co-Founder and Chief Executive Officer Beenu Arora, Ingram will drive enterprise execution as the company continues enhancing its AI-native cybersecurity architecture across threat intelligence, dark web visibility, digital risk protection, endpoint monitoring, and agentic AI systems.
Significance of Cyble Executive Vice President US
The appointment of the Cyble Executive Vice President US is significant for the enterprise cybersecurity and threat intelligence sectors because North American organizations face an escalating volume of automated ransomware attacks, software supply chain compromises, and credential theft operations. Navigating the highly competitive United States market requires specialized technical capability combined with executive-level trust across heavily regulated industries.
Transitioning an experienced leader from an advisory capacity directly into active business operations reflects Cyble’s aggressive investment in capturing enterprise market share. Ingram’s background directing cyber practices at EY and PwC provides practical insight into how chief information security officers (CISOs) and board audit committees evaluate vendor risk, compliance mandates, and automated incident response systems.
Furthermore, modern security operations centers (SOCs) are increasingly turning toward agentic AI architectures capable of analyzing telemetry and mitigating exposures autonomously. Pairing advanced dark web and digital risk monitoring with seasoned leadership that understands institutional banking, critical infrastructure, and law enforcement frameworks ensures Cyble can deliver actionable, decision-ready threat intelligence to Fortune 500 enterprises and government agencies.
Next Steps for Cyble Executive Vice President US
Following his transition to Executive Vice President US, Ingram will focus on expanding dedicated sales and solution engineering teams across major American commercial centers. He will engage strategic systems integrators and enterprise security leaders to accelerate customer adoption of Cyble’s automated risk intelligence platform.
Looking ahead, Cyble will continue expanding its artificial intelligence capabilities, deploying new agentic workflows designed to automate external attack surface management and threat neutralization. Technical engineering teams will work closely with American client organizations to provide continuous digital risk visibility and preemptive dark web monitoring.